From Technology Audit to a 90-Day Roadmap: Turning Findings Into Action
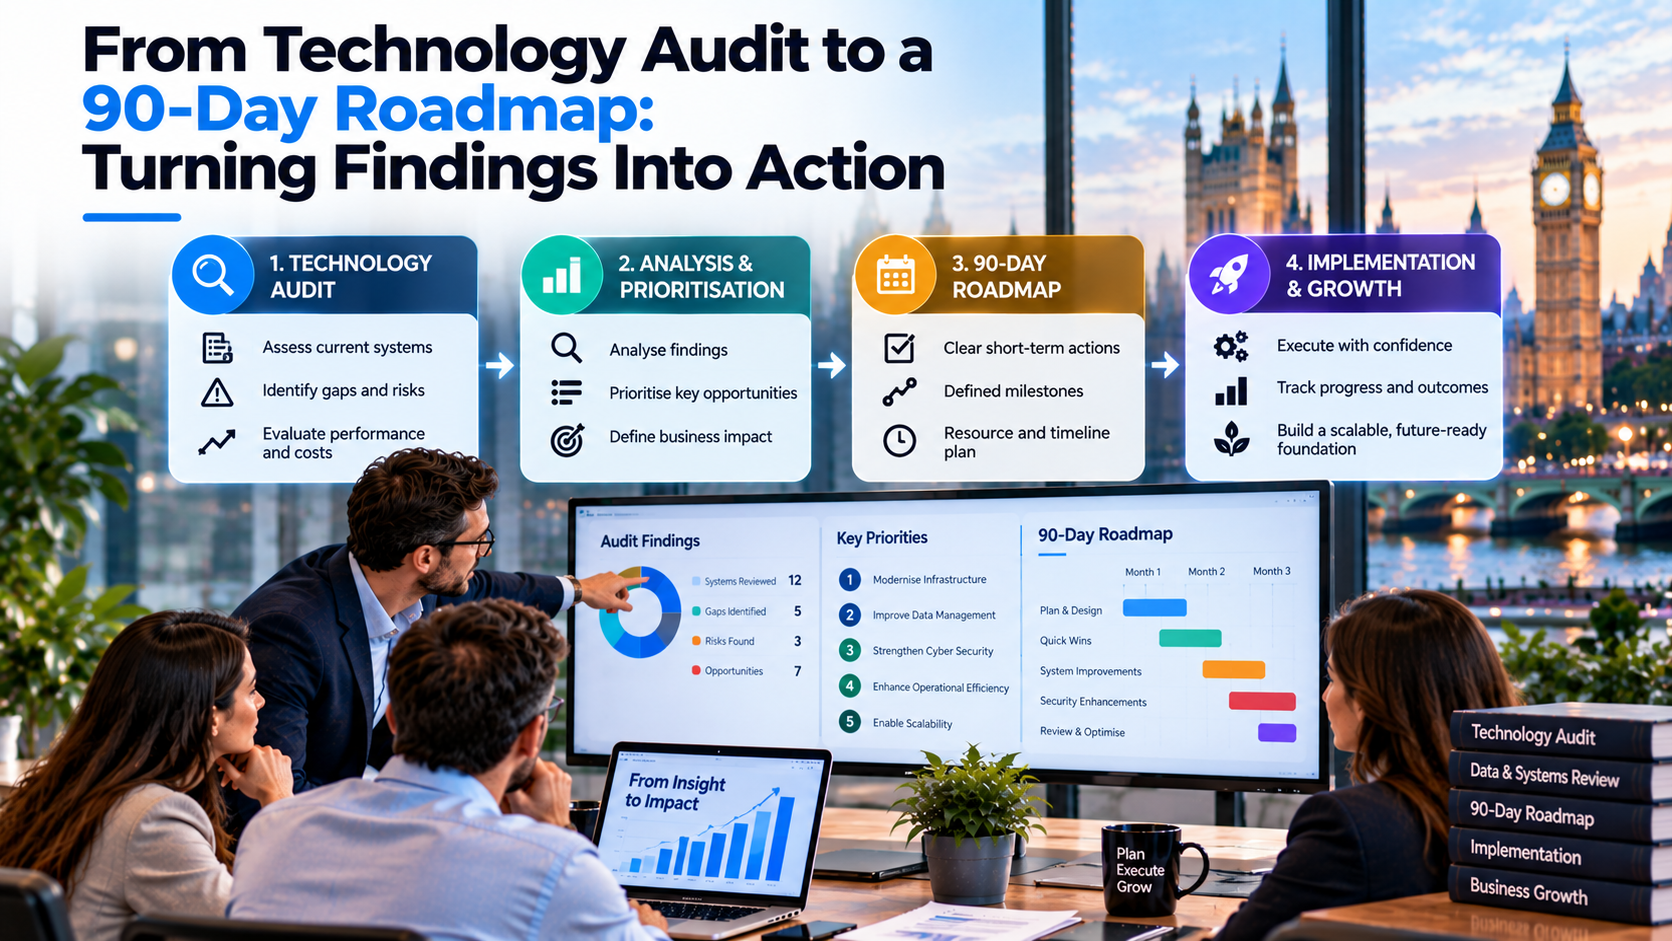
A technology audit only creates value when findings become action. Learn how UK businesses can turn audit results into a prioritised 90-day technology roadmap.
A technology audit can reveal a surprising number of issues: manual processes, disconnected systems, outdated applications, reporting gaps, security risks and opportunities for automation. The difficult part begins after the findings are documented. A long list of recommendations does not tell a business what to do first. That is why a prioritised roadmap is one of the most important outputs of an effective audit.
The first step is to establish a baseline. Leaders need to understand the current cost, risk and operational impact of each issue. A manual workflow might consume several hours each week. A disconnected system might cause reporting delays. An unsupported application might create security or continuity risk. Quantifying the problem helps the organisation compare different investments rather than choosing projects based on who asks the loudest. For further context, see Nexteck technology audit.
The next step is prioritisation. Nexteck’s published methodology uses impact and urgency to score technology opportunities and sequence them into a roadmap. This is a useful principle because it prevents the organisation from treating every recommendation as equally important. A high-impact, urgent issue should normally receive attention before a low-impact improvement that is simply easier to implement.
A 90-day roadmap can be divided into quick wins, foundation work and larger initiatives. Quick wins might include removing duplicate manual reporting, improving access controls or documenting a critical process. Foundation work could involve cleaning data, defining system ownership or creating an integration plan. Larger initiatives may require a new platform, custom software or a major architecture change and should be prepared rather than rushed. For further context, see Nexteck AI opportunity planning.
Each action should have an owner, a target outcome and a way to measure progress. Technology projects often become difficult to evaluate because the organisation measures whether the software was delivered rather than whether the business improved. A better approach is to connect projects to operational metrics such as processing time, error rates, response speed, conversion, service quality or management reporting time.
Governance keeps the roadmap alive. A monthly or weekly review should check what has changed, what is blocked and whether priorities need to move. Nexteck’s KPI governance approach focuses on reviewing targets against actuals and using exceptions to direct management attention. This turns the roadmap from a static document into part of the operating rhythm.
Security and compliance actions should also be integrated into the roadmap rather than isolated at the end. The ICO’s guidance encourages organisations to build data protection into processing activities, while NCSC guidance covers areas such as risk management, architecture, identity, data security and incident management. These references can help businesses structure their technology improvement plans responsibly. For further context, see NCSC cyber security framework.
The strongest 90-day roadmap is therefore not a shopping list of software. It is a sequence of business improvements supported by technology. When priorities are costed, owned and measured, leaders can make clearer decisions about what to fund, what to delay and what to stop doing. That is the practical difference between having an audit and actually using one to change the business. For further context, see Nexteck UK architecture.